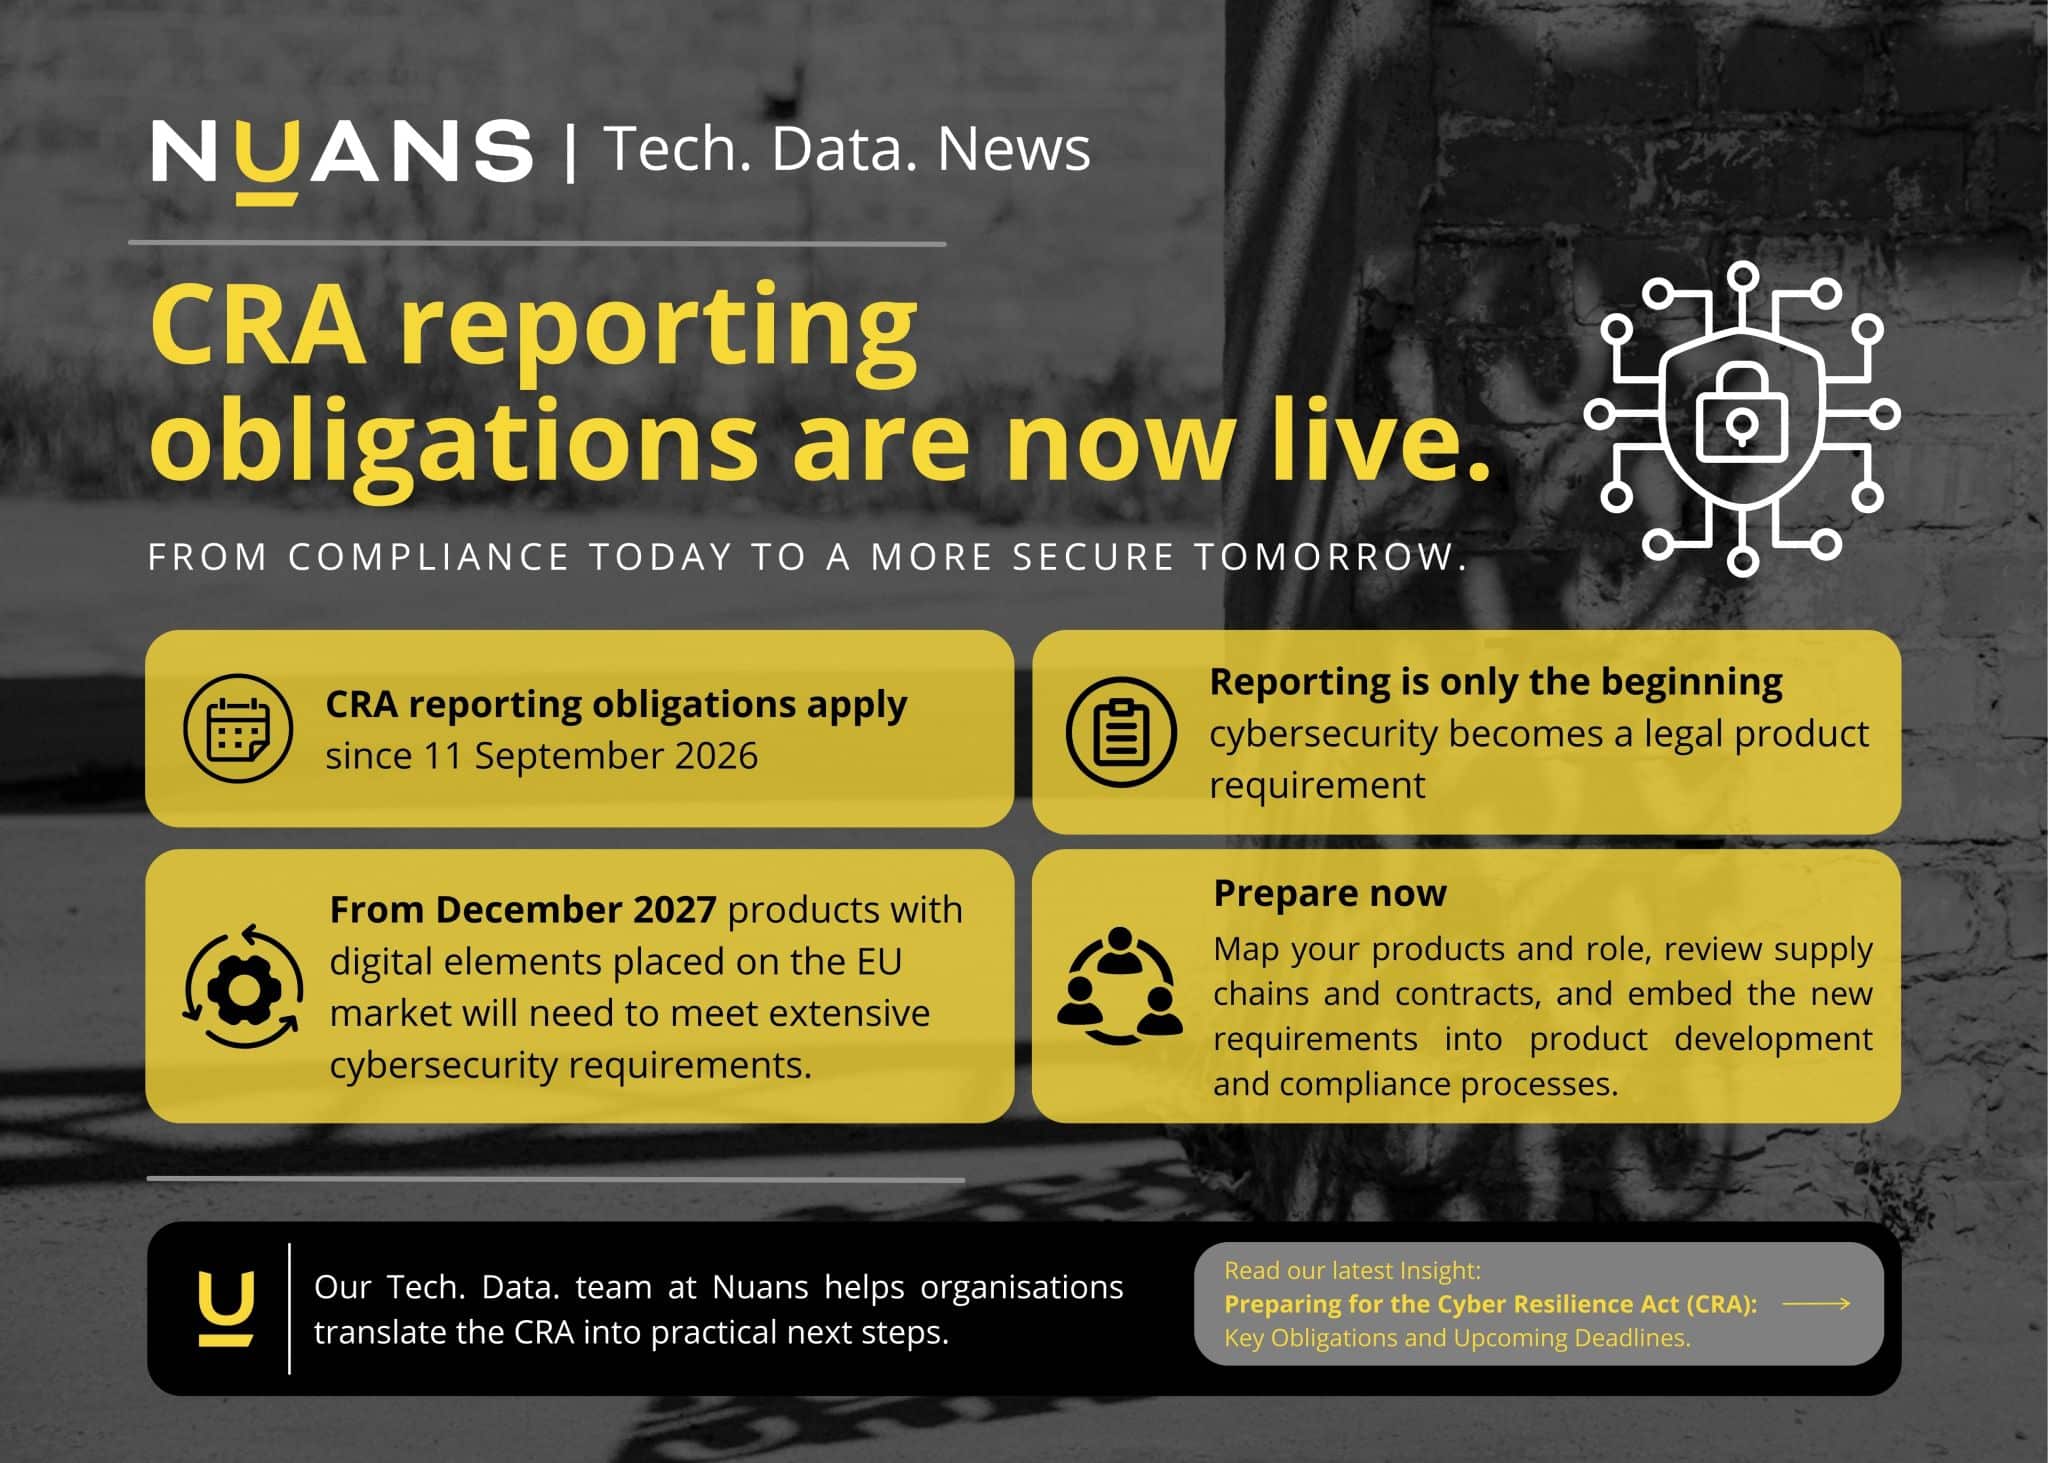

Since 11 September 2026, the Cyber Resilience Act (CRA) reporting obligations have applied to affected manufacturers – including a strict 24-hour deadline for an early warning after becoming aware of an actively exploited vulnerability or severe incident.
But reporting is only the beginning.
The CRA fundamentally changes how cybersecurity is addressed for products with digital elements: cybersecurity becomes a legal product requirement throughout the product lifecycle.
From December 2027, products with digital elements placed on the EU market will need to meet extensive cybersecurity requirements – from secure design and vulnerability handling to security updates and ongoing support.
The CRA also raises the bar on transparency towards users, requiring clearer information on product security, secure use and the period during which security support will be provided.
What this means in practice depends on your organisation’s role – whether you are a manufacturer, importer or distributor.
December 2027 may still seem some way off. But preparing for it starts today: mapping your products and role under the CRA, reviewing supply chains and contracts, and embedding the new requirements into product development and compliance processes.
Our Technology. Data. team at Nuans helps organisations translate the CRA into practical next steps.
Want to dive deeper? Read our Insight: “Preparing for the Cyber Resilience Act (CRA): Key Obligations and Upcoming Deadlines.”